The core difference
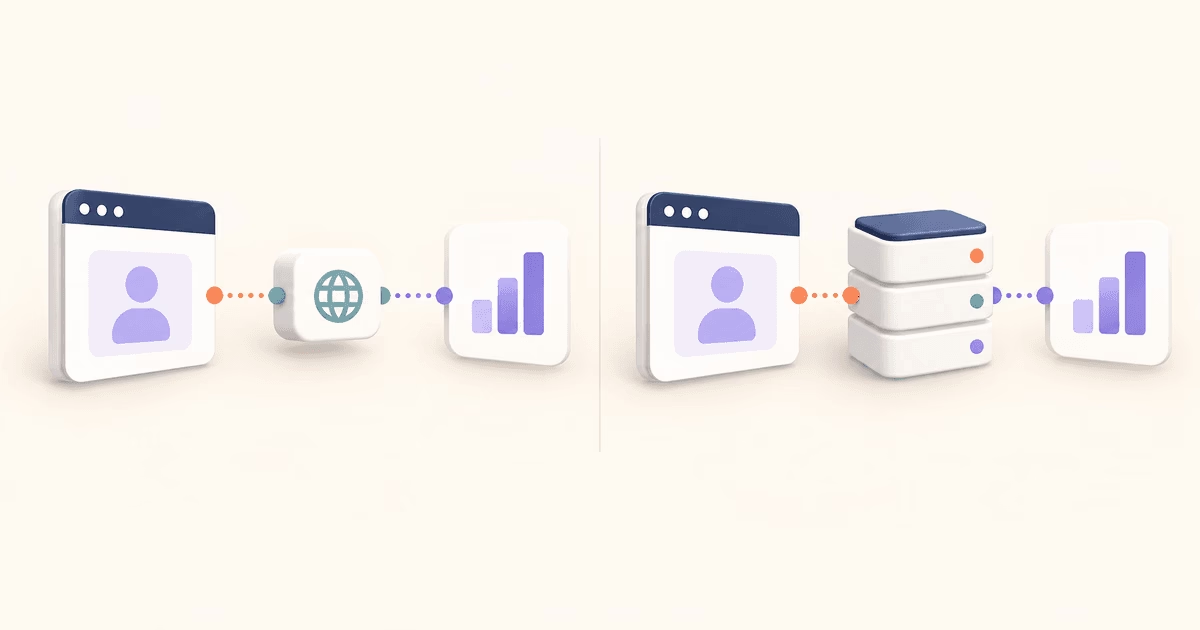
Server-side GTM and Introtrace start from opposite ends of the same problem, and which one you need mostly comes down to which end is actually broken for you.
Server-side GTM
Moves tag execution from the browser to a server you control. Browser-based measurement uses a client such as GTM or gtag.js to send events to the server container. The container can also receive app and server-to-server events, then process and route them using its configured tags.
Introtrace
Keeps your existing analytics setup untouched. A lightweight client-side script monitors for blocked signals. When an ad blocker prevents a request to GA4, GTM, Facebook, or any other provider, Introtrace reroutes only that blocked signal through the shared CDN, or your configured subdomain on a paid plan.
In a browser setup using web GTM, the container collects events and sends them to your tagging server. Server-side tags can then filter, enrich, and route those events. Other inputs, including apps and backend services, can send events without that web container.
The catch is that there are three separate layers where data can fail, and sGTM only reaches one of them well. Layer one is the network: does the browser's initial request even leave the device, or does an ad blocker intercept it before it reaches your tagging server? Layer two is consent: does the visitor's consent state allow collection at all? Layer three is attribution: once data does arrive, is it clean enough to act on? sGTM handles layers two and three genuinely well — enrichment, consent enforcement, first-party cookies. Layer one isn't reachable from there at all; it happens upstream of the server container.
A web GTM container is one possible browser client, rather than a requirement for every server-side setup. Google also documents gtag.js, app, and server-to-server inputs. See Google’s server-side tagging overview. Check the input path your integration actually uses.
Side-by-side comparison
| Feature | Introtrace | Server-Side GTM |
|---|---|---|
| Setup time | Under 2 minutes — paste one script tag | Hours to days — provision cloud infra, configure container, set up custom domain |
| Infrastructure required | None — fully managed SaaS | Google Cloud Run / AWS / custom server |
| Monthly cost | $9.99/month for up to 100K recovered requests | Depends on hosting, request volume, and network usage |
| DevOps / engineering effort | Managed service — no server to manage | Ongoing — server monitoring, scaling, updates |
| Ad blocker recovery approach | Shared CDN recovery; custom subdomain on paid plans | Configure first-party script serving and event routes; test coverage |
| Works when GTM loader is blocked | Yes — detects blocked signals independently | Browser inputs depend on the configured loader; other input paths differ |
| Supports non-GTM analytics | Yes — GA4 standalone, Meta Pixel, Mixpanel, Amplitude, etc. | Clients and tags receive and route supported event formats |
| Server-side data enrichment | No — pass-through proxy by design | Yes — modify/enrich events before forwarding |
| Server-side consent enforcement | No — relies on client-side consent | Yes — can enforce consent rules server-side |
| First-party cookie control | Uses existing cookies — no new cookies set | Full control — can set first-party cookies from server |
| GDPR / privacy compliance | Limited metadata retained; customer consent responsibilities apply | You configure consent, processing, retention, and security |
| Geographic data accuracy | Verify forwarded visitor context and provider reporting | Verify the context received and forwarded by your server tags |
Why the GTM loader is the weak link
People assume moving tags to the server automatically fixes ad blocker data loss. It doesn't — the client-side loader has to run first, and that's exactly where things fall apart:
- A visitor with uBlock Origin arrives at your site.
- Your page tries to load
googletagmanager.com/gtm.js. - uBlock blocks the request. The GTM loader never executes. Your server container receives nothing.
This example applies to browser events collected through a blocked web GTM loader. Other client and server-to-server paths differ. Google also provides first-party script serving through Google tag gateway.
A custom loader changes where the browser downloads the script. Check both the loader and the outbound event requests: a successful script download alone does not establish that events reached your server container.
Introtrace addresses blocked script downloads and outbound event requests separately. Add it directly to the page head, before analytics and consent scripts. Recovery uses the shared CDN by default, with a custom subdomain available on paid plans.
When to use each
Use Introtrace when…
- • Your primary goal is recovering data blocked by ad blockers
- • You want a zero-infrastructure, zero-DevOps solution
- • You use analytics tools outside the GTM ecosystem (Mixpanel, Amplitude, Segment)
- • You need to be live in under 2 minutes
- • You're a small-to-mid-size business without a dedicated data engineering team
If your priority is recovering blocked browser requests, evaluate Introtrace against that requirement. If you also need server-side event processing or enrichment, evaluate a server container or a combined setup. Base the decision on measured recovery and operational needs.
Use server-side GTM when…
- • You need server-side data enrichment and transformation
- • You want server-side consent enforcement
- • First-party cookie control is a priority
- • You have DevOps resources to manage cloud infrastructure
- • Your organisation is large enough to justify the cost and complexity
Data quality and control, not ad blocker bypass, are what justify sGTM's complexity. Legal requiring that PII never reaches a third-party server unredacted, or an attribution model that depends on server-side enrichment with CRM data — that's the pipeline sGTM builds. You'll still have the loader problem to solve separately, which is exactly the gap Introtrace fills alongside it.
Use both when…
Want sGTM's processing power and additional browser-request recovery? Evaluate both together. Verify that the loader runs, events reach your container, and its tags forward them as intended. Check consent behavior and deduplication before relying on the combined reports.
Real-world setup: what each looks like
A feature table tells you what each option can do; it says nothing about what a Tuesday afternoon spent setting one up actually feels like. Here's that part, for a typical marketing or analytics team.
Server-side GTM setup
- Create a Google Cloud project and enable billing
- Enable Cloud Run and Container Registry APIs
- Deploy the GTM server container image (
gcr.io/cloud-tagging-10302018/gtm-cloud-image) - Configure a custom domain and provision a TLS certificate
- Update client-side GTM container to point to your server container URL
- Configure server-side tags, triggers, and variables in GTM UI
- Set up monitoring, alerting, and auto-scaling policies
- Ongoing: update container image, monitor spend, tune instance counts
Setup and maintenance time depend on the deployment and event configuration. Include monitoring, consent checks, and recovery testing in your estimate.
Introtrace setup
- Sign up at introtrace.com
- Copy your unique script tag from the dashboard
- Place it near the start of your site's
<head> - Trigger a test event with your blocker enabled and confirm receipt in your analytics tools
Estimated time: under 2 minutes. Verify recovery when your tags or blocker configurations change.
That time gap is really about who's allowed to close it. sGTM setup wants someone fluent in Google Cloud IAM, container orchestration, DNS, and TLS certs — which for most marketing teams means filing a ticket with engineering and waiting for a slot on their calendar. Introtrace just needs someone who can edit a <head> tag, so the person who actually noticed the analytics gap can go fix it themselves.
Frequently asked questions
Is server-side GTM better than a first-party proxy for ad blocker bypass?
The result depends on the loader and event routes you configure. A server container can receive browser, app, or server-to-server events. For browser events, verify both script delivery and the request to the server container. Introtrace addresses supported blocked scripts and event requests; compare recovery using the same test setup.
How much does server-side GTM cost compared to Introtrace?
Server-side GTM costs depend on hosting, traffic, and operational needs. Introtrace is free up to 20,000 signals per rolling 30 days, with paid plans at $9.99/month for 100,000 signals and $19.99/month for 500,000. Compare the billable request volumes, not just visitor counts.
Can I use Introtrace and server-side GTM together?
Yes. A server container can process and route events, while Introtrace can help recover supported blocked browser requests. Verify the combined loader and event path, consent settings, and duplicate handling on your own setup.
Does sGTM affect page load speed?
A browser-side loader still runs when client-side events are sent to a server container. Its performance depends on the scripts, triggers, and deployment. Introtrace also adds a browser script; compare field and lab performance before and after changing either setup.
What happens to my sGTM data if the server container goes down?
Requests may fail while the server container is unavailable. Recovery depends on your client’s retry behavior and any queueing or fallback you implement. Monitor delivery failures and test your outage handling; neither managed hosting nor a recovery proxy guarantees delivery during every outage.